A hacker gained access to 8.8 million CPR numbers and personal data of Danes, which has been considered a serious incident, and an investigation is being conducted by the police. #wyciekdanych #Cyberbezpieczeństwo #Dania (translated)
A hacker gained access to 8.8 million CPR numbers and personal data of Danes, which has been considered a serious incident, and an investigation is being conducted by the police. #wyciekdanych #Cyberbezpieczeństwo #Dania (translated)

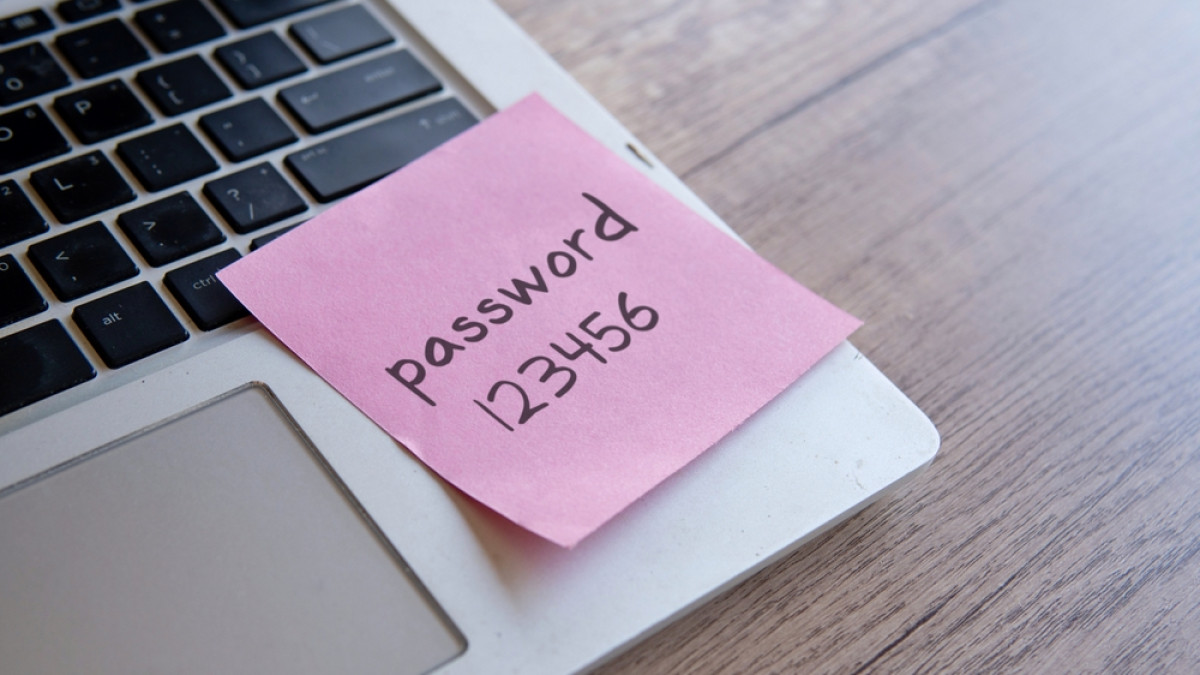
Claus Due wrote that a CPR leak allegedly originated from a company in Funen, where an employee had been hacked. He claimed that the employee's password was 123456 and that there was no two-factor authentication. Due pointed out that the company marketed itself with "top secure data protection," but according to him, apparently did not have sufficient requirements for passwords or monitoring of access. He assessed that the company would be finished when its name became known, a bill arrived, or a fine was issued – or if all three things happened. #datasikkerhed #hack #cybersikkerhed (translated)
An anonymous hacker claims to have cracked the Danish CPR registry with the leaked password "123456" and has shared over 8.7 million personal identification numbers while expressing shock at the security shortcomings. #hackare #Dataintrång #Danmark (translated)

Almost a million Danes have created a warning after the leak of CPR information. (translated)
The number of Danes who have set up a credit warning after the CPR leak has dramatically increased to almost 970,000 in a week to protect themselves against identity theft. #CPRlæk #Kreditvarsel #Identitetsbeskyttelse (translated)
Lars Andersen wrote that he had spent over a year in closed prison after sharing a couple of CPR numbers and offering a reward for the Minister of Justice's health journal. He sarcastically added that it apparently was much worse than murder. https://t.co/1szirRnAhF #retssystem #fængsel #justits (translated)
CPR leakage can lead to rising costs for companies, as they have to invest in improved data security and handling of personal information. (translated)
Claus Due wrote that the CPR leak had led to 14 million inquiries over the ten days it lasted, equivalent to an average of 16.2 inquiries per second around the clock. He added that no alarms had gone off. #CPR #data #overvågning (translated)
Pharmacists have increased their attention after a leak from the CPR register, raising concerns about data protection and patient confidentiality. (translated)
Pharmacists can now ask verification questions to patients after a leak of CPR data to protect their personal information. (translated)
After a leak of information from the CPR register, pharmacies are tightening their controls when dispensing medication, especially those with abuse potential, which may result in citizens needing to present ID or answer control questions. #CPRlæk #Apoteker #Medicinkontrol (translated)
After a leak of information from the CPR register, pharmacies will increase their vigilance when dispensing medication, especially those with potential for abuse, and can now ask control questions and require ID to ensure correct dispensing. #CPRlæk #Apoteker #Medicinkontrol (translated)
Cyberhotline extends its opening hours to assist citizens after a leak of personal sensitive information from the CPR register. (translated)
The minister does not rule out the possibility of issuing new CPR numbers in the wake of the leak. (translated)
A cyber attack in Denmark affected 8.8 million people due to the leak of data from the national register, including names, addresses, and CPR numbers. #ScurgereDeDate #AtacCibernetic #Danemarca (translated)

Mitchel Oliver wrote that the Parliament would open the day after, even though the political season had not yet begun. He mentioned the drone scandal, the CPR scandal, the fingerprint scandal, relaxations of citizenship rules, a proposal for a sneaky tax, L5 taxes on vegetables, and what he described as the worst PISA results ever. Oliver wrote that the government had already grossly failed the Danes. #Folketinget #politik #Danmark (translated)
In Denmark, a serious security incident occurred after unauthorized individuals gained access to personal data of 8.8 million people, including names, addresses, and CPR numbers. #Danska #curenjePodataka #sigurnost (translated)
Claus Due urged readers to read an article and wrote that the state's security measures had not reacted to the fact that an otherwise legal access to the CPR register had suddenly made 8.8 million queries. He claimed that the activity had been perceived as regular use. https://t.co/S8eL8NIMPW #sikkerhed #data #CPRregister (translated)
In Denmark, there was a major hacking attack during which the data of 8.8 million people was stolen, including names, addresses, and CPR numbers, and an investigation into the incident is ongoing. #Danska #hakerskiNapad #curenjePodataka (translated)
Klaus Riskær Pedersen criticized the former and current government for the handling of the CPR register. He wrote that systematic data collection could have taken place without being stopped by the security systems and called it a political scandal that required immediate accountability. Pedersen claimed that the problems were due to Minister of Interior and Housing Christian Rabjerg Madsen awarding the operation of the CPR system to the American company DXC Technology in 2022. He also criticized former Minister Kaare Dybvad Bek, stating that the tender in 2021 was carried out under the GPA agreement, which allowed American companies to bid. According to Pedersen, the agreement allowed for the exclusion of foreign bidders on grounds of security and vital national interests, and he believed that the CPR register, which he described as critical infrastructure, should not have been entrusted to a foreign company. He placed the responsibility for the lack of control systems on the Agency for Digitization and believed that the government's leadership bore political accountability for the appointments. He wrote that Prime Minister Mette Frederiksen had not made the decision herself but had appointed a political leadership that he considered lacking in professionalism and experience. He also claimed that the government had been so preoccupied with the war in Europe by the end of 2022 that it had not concerned itself with the CPR system. Furthermore, Pedersen criticized that the Parliament, in his opinion, would choose Henrik Frandsen from the Moderates as chairman, even though Frandsen had only served in Parliament for four years. He described Frandsen as unworthy of the position and accused him of serious moral shortcomings. Pedersen wrote that all Danish citizens must remain vigilant until those responsible figured out whether new CPR numbers were necessary, suggesting that Russia would be to blame. He alleged that businesses' access to the register had been shut down, causing chaos, and that the lack of identity verification could make it difficult for public institutions to hire educators. He compared the situation to previous problems in the police's data systems. #Inkompetence #Politik #Danmark (translated)